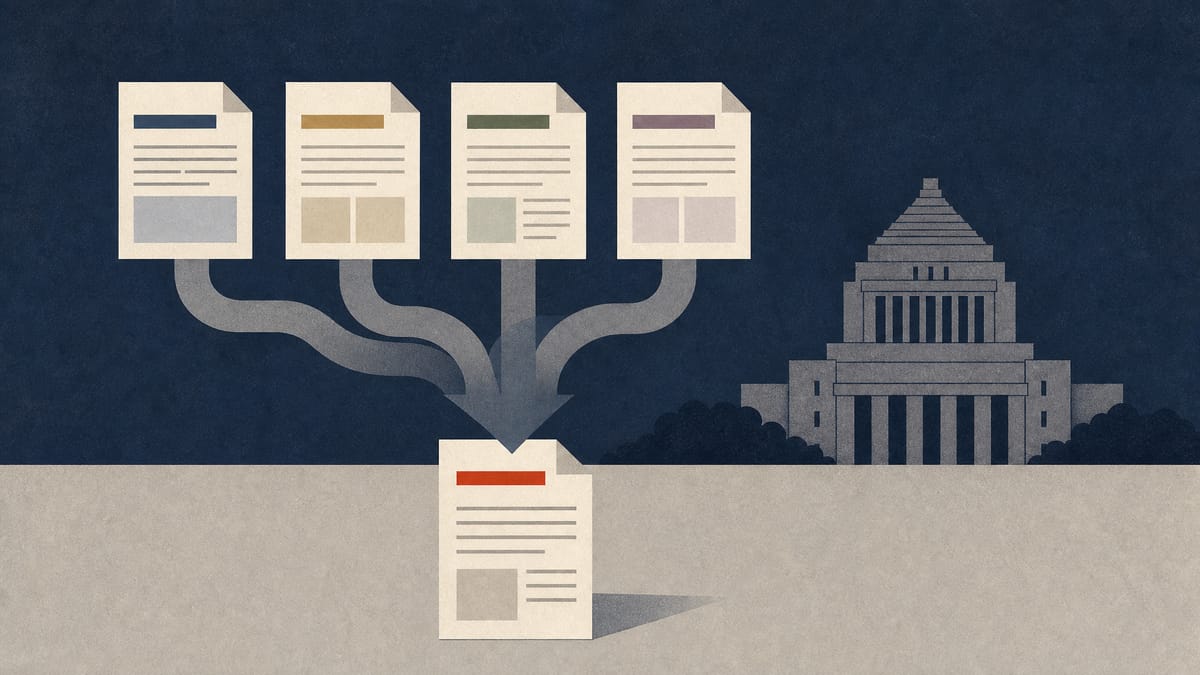
Japan's privacy watchdog wants to stop cyberattack victims from filing the same incident report over and over to different ministries.
On July 16, 2026, the Personal Information Protection Commission opened a monthlong public comment period on a draft amendment to the notification that governs how businesses and government bodies report personal-data breaches and My Number leaks. The proposal does not touch the underlying duty to report. Businesses still must notify the PPC when they leak personal data under Article 26 of the Act on the Protection of Personal Information, government bodies must report under Article 68, and organizations handling My Number data must report under Article 29-4 of the Number Act. What changes is how they can file when the incident is a cyberattack.
Right now, those reports normally have to go through the PPC's own electronic reporting system, the online portal on its website, unless a network outage, disaster or similar reason makes that impossible. Last year, after complaints that ransomware victims were stuck filing similar paperwork to multiple government offices in the middle of incident response, an interagency agreement dated May 28, 2025 let them use a shared Ransomware Case Common Form instead.
The new draft extends that logic. Following the enactment of Japan's Act on Prevention of Damage from Wrongful Acts against Critical Computers (Law No. 42 of 2025), the interagency agreement is being revised to add an Other Cyberattack Incidents Common Form covering cyberattacks beyond ransomware, and to create a public-private coordination platform, run by the National Cyber Office, that accepts reports required under Article 5 of that law. Under the amendment, organizations reporting a qualifying cyberattack to the PPC or the relevant sector minister could use the new common form as an alternative to the electronic portal, and could file either the ransomware form or the new cyberattack form directly through the coordination platform instead of going agency by agency.
| Milestone | Date |
|---|---|
| Public comment period opens | July 16, 2026 |
| Public comment period closes | August 14, 2026 (23:59 JST) |
| New cyberattack common form takes effect (scheduled) | October 1, 2026 |
The PPC is taking comments through August 14, 2026, and cautions that the final rule may differ from the draft. The changed notification is timed to take effect October 1, 2026, the same day the new Other Cyberattack Incidents Common Form is meant to go live, and the amended rule is set to stay in force indefinitely once it takes effect. The overview reviewed here does not spell out what qualifies as an "other cyberattack incident" beyond distinguishing it from ransomware, so companies will need the full interagency agreement text to know exactly which incidents the new form covers.